Ransomware: How One Small Incident Can Shut Down a Business
by Daniil Slesarenko
It Can Start With One Click
A ransomware attack does not always begin with a major security failure.
It can start with one employee opening a malicious attachment, entering credentials into a fake login page, or downloading a compromised file.
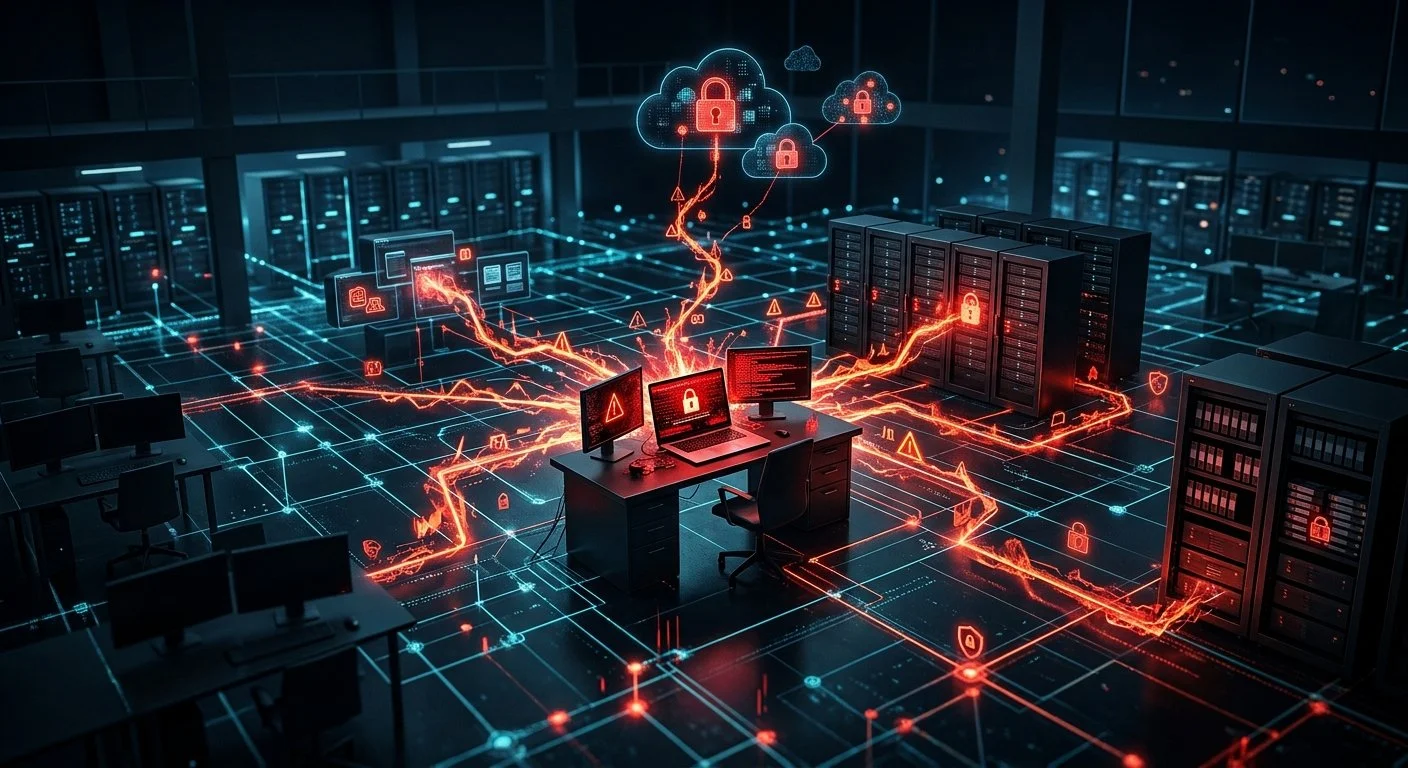
At first, the incident may appear to affect only one computer. But if an attacker can gain access to additional accounts and systems, that small incident can quickly become a much larger problem.
The goal of ransomware is not simply to infect one computer. Attackers want to disrupt enough of an organization's environment to make the business feel the impact.
How a Ransomware Attack Spreads
Once an attacker gains access, they may spend time looking around the environment before deploying ransomware.
They can attempt to obtain additional credentials, identify important servers, discover shared files, and determine which systems are connected to critical business operations.
This reconnaissance allows attackers to identify what will cause the most disruption.
An attack might progress from:
One compromised device → Additional credentials → Internal systems → Critical infrastructure → Widespread encryption
The longer an attacker has access, the more opportunities they may have to expand their reach.
Why One Computer Can Become a Business Problem
Modern businesses rarely operate as isolated computers.
Employees depend on shared file servers, databases, cloud applications, authentication systems, business applications, and network services. If several of these systems become unavailable, employees may be unable to do their jobs even if their individual computers are still functioning.
For example, a ransomware incident could prevent employees from accessing:
Customer and business records
Shared documents and file servers
Accounting or financial systems
Business applications
Email and collaboration tools
Critical operational systems
The result can be much more than lost files. It can become a business interruption.
The Attacker May Target Backups Too
Backups are one of the most important defenses against ransomware, but attackers know this.
If backup systems are accessible from the same environment, an attacker may attempt to delete, encrypt, or otherwise compromise them before deploying ransomware.
This is why having a backup is not necessarily the same as having a reliable recovery strategy.
Organizations need to know whether their backups are protected from the systems they are backing up, whether previous versions can be recovered, and whether the recovery process has actually been tested.
A backup that has never been restored is a plan that has never been proven.
What Happens When Systems Go Down?
Once ransomware is deployed, the organization may suddenly lose access to systems it depends on every day.
Employees may be unable to access files. Customer services may be interrupted. Orders may stop processing. Financial operations may be delayed.
IT teams then have to work under pressure to determine what happened, contain the attack, identify affected systems, preserve evidence, and begin recovery.
At the same time, business leaders may need to make decisions about communications, customers, vendors, legal obligations, and the organization's ability to continue operating.
The technical incident quickly becomes a business crisis.
How Organizations Can Reduce the Impact
Preventing every ransomware attack is difficult, but organizations can make it much harder for an incident to become a major outage.
Some important controls include:
Strong authentication and multi-factor authentication
Regular security updates and vulnerability management
Network segmentation and appropriate access controls
Endpoint protection and monitoring
Reliable, protected backups
Least-privilege access
Employee security awareness training
A documented and tested incident response plan
These controls work together. There is no single tool that guarantees protection from ransomware.
Don't Wait Until the Systems Are Down
The worst time to discover that your backups don't work, your monitoring isn't configured, or nobody knows who is responsible for responding to an incident is during a ransomware attack.
Organizations should prepare before something happens.
Know what systems are critical. Know who has access to them. Know where your backups are stored. Know how they would be recovered. Most importantly, know what your team will do when the first signs of an attack appear.
Ransomware can begin with one compromised account or device, but the consequences can extend across the entire business.
The goal isn't just to prevent ransomware. It's to make sure one incident cannot bring the whole organization to a standstill.