What Happens After Your Password Is Stolen?
by Daniil Slesarenko
A Stolen Password Is Only the Beginning
Most people think of a stolen password as a problem that affects one account. In reality, it can be the starting point for a much larger attack.
Once an attacker has a working username and password, they can attempt to access email, cloud services, business applications, and other systems connected to the account. If the same password is used elsewhere, the attacker may try it on those accounts too.
The danger isn't just losing access to one account. It's what an attacker can do with that access.
How Attackers Get Stolen Passwords
Passwords can be obtained in many ways. Phishing attacks, data breaches, malware, password reuse, and compromised websites can all expose credentials.
Attackers may also purchase stolen credentials from other criminals or use automated tools to test usernames and passwords against different services.
Common sources include:
Phishing emails and fake login pages
Previous data breaches
Reused passwords from another account
Malware that captures credentials
Stolen credentials being sold or shared online
Once credentials are obtained, attackers can begin testing whether they still work.
What Happens Next?
The attacker will often try to log in as the legitimate user. If the password works and additional security controls do not stop the login, the attacker may gain access to the account.
From there, they may look for useful information such as emails, documents, contacts, financial information, or additional credentials.
A compromised email account is particularly valuable because it can be used to reset passwords for other services and impersonate the victim.
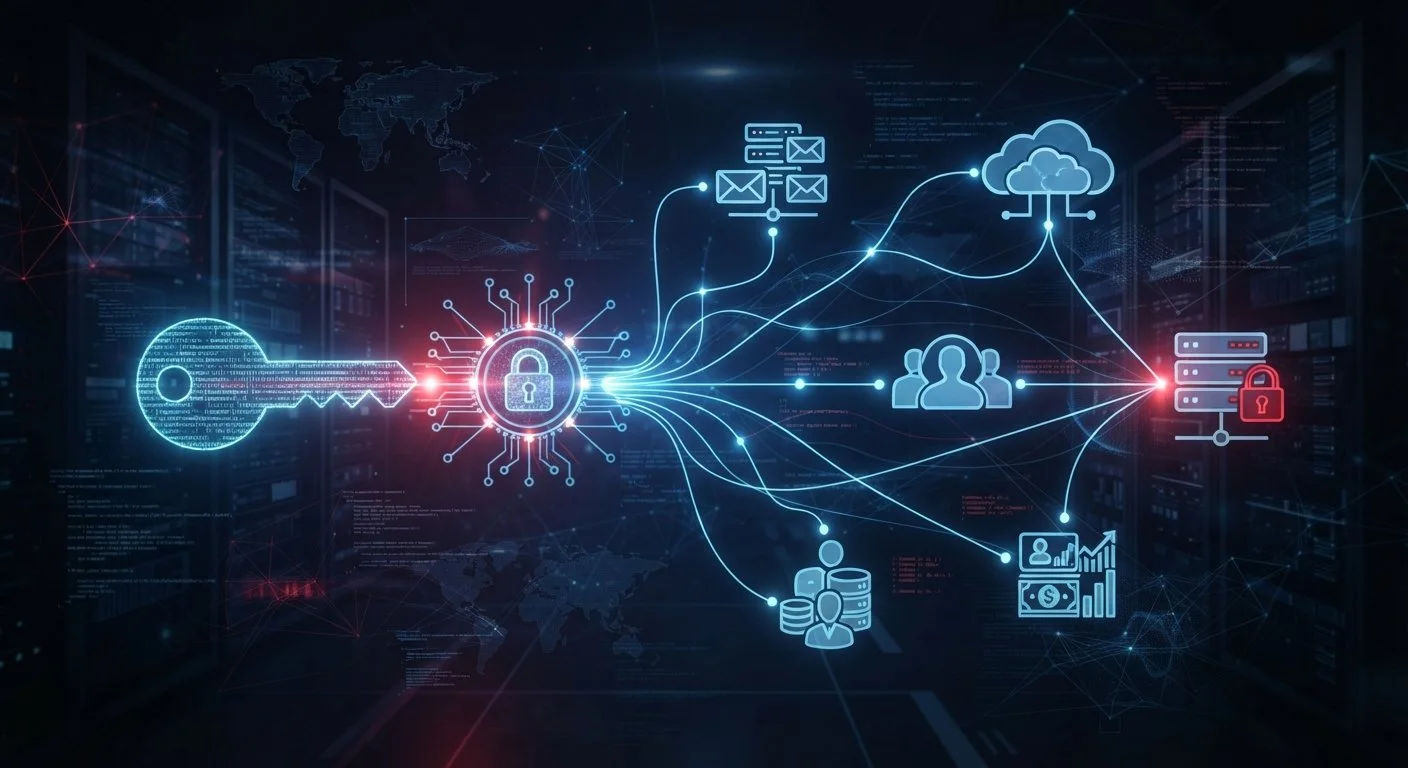
The attack can quickly become a chain:
Stolen password → Account access → Information gathering → Further account compromise
Why Password Reuse Makes Things Worse
Using the same password across multiple services gives attackers more opportunities.
For example, a password stolen from a personal website could potentially be tested against a work email account. If the same credentials work, a relatively small breach can become a business security incident.
This is one reason unique passwords are so important. A compromised password should ideally expose only the account where it was originally used.
A password manager can make it much easier to create and maintain unique passwords without requiring users to remember dozens of different combinations.
What Happens When a Business Account Is Compromised?
A compromised business account can create risks beyond the individual employee.
An attacker may be able to access company email, internal documents, customer information, or business applications. They may also use the account to send convincing phishing messages to coworkers or customers.
This can turn one compromised account into a stepping stone toward additional systems.
Organizations can reduce this risk by combining unique passwords with multi-factor authentication, access controls, monitoring, and employee security awareness.
What You Should Do If Your Password Is Stolen
If you believe a password has been compromised, acting quickly can limit the damage.
Change the password immediately, and change it anywhere else that the same password was used. Review recent account activity and terminate unfamiliar sessions where the service provides that option.
For business accounts, notify your IT or security team rather than trying to handle the incident alone.
Important steps include:
Change the compromised password
Change reused passwords on other accounts
Enable or verify multi-factor authentication
Review recent login and account activity
Report suspected compromises to your IT or security team
The faster a compromised credential is identified and contained, the less opportunity an attacker has to use it.
Don't Let One Password Become the Master Key
A stolen password doesn't automatically mean an attacker has control of everything. Strong authentication, unique passwords, monitoring, and quick response can prevent a compromised credential from becoming a much larger incident.
The important thing is to treat a stolen password as the start of a security incident, not simply as a reason to change one password.
Your credentials are one of the keys to your digital environment. Make sure one stolen key cannot open every door.